Execute remote command (SSH)
This example shows how to run commands on a remote host from an OnSphere script using SSH with PEM-format key authentication.
Create a detached script scheduled to run every 30 seconds.
Write a JavaScript script that opens an SSH connection and executes a command on the remote host.
Generate an RSA key pair in PEM format and register both files as module resources.
Deploy the public key to the remote host’s
authorized_keysfile to enable key-based authentication.
git checkout origin/osp-scripts-configuration .
git checkout origin/example-scripts-execute-remote-command .
Configuration
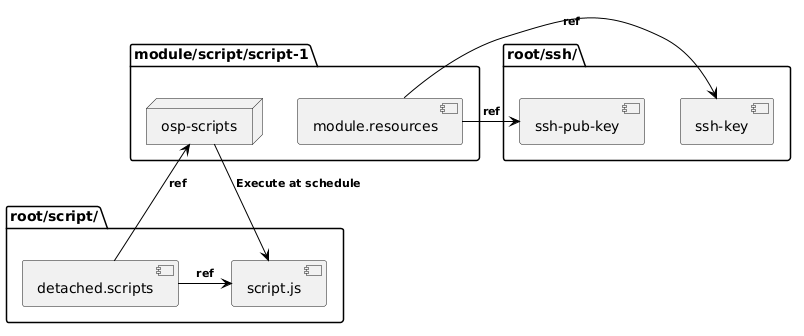
Steps
1. Create a detached script
root/script/detached.scripts
The detached script has the task to execute the script every 30 seconds.
{
    "moduleId" : "modules.scripts.scripts-1",
    "sourceFile" : "root/script/script.js",
    "accessedValues" : [],
    "scheduledExecutions" : ["0/10 * * ? * * *"]
}
1. Create a script to execute on a remote target (via SSH)
root/script/script.js
Note
Change the IP/hostname and check if the SSH is enabled on your test target.
main();

function main() {

    log.info("Execute example script with schedule execution and certificate authentification");
    // Create the runner for SSH with CERTIFICATE
    let runner = ssh.certCmdBuilder("10.100.0.77", 51234, "osp", "test")
    // Set the maximum time to establish the connection (keep it low)
    .setConnectionTimeout(5)
    // Set a maximum time after witch the SSH drop the line.
    .setMaxCommandTime(5)
    .build();

    // Establish a SSH connexion and run a command.
    let res = runner.run(["echo \"executed\"", ">", "/tmp/script-execution-result"]);

    // If SSH failure
    if (res.exceptionCode !== 0)
    {
        log.error("Fail to establish the SSH connection with error code [" + res.exceptionCode + "]");
        return;
    }

    if (res.returnCode !== 0)
    {
        log.error("Fail to execute the command error code [" + res.exceptionCode + "] and stdin [" + res.stdIn + "] and stderr [" + res.stdErr +"]" );
        return;
    }

    log.info("Execution success output is [" + res.stdIn + "]");
}
3. Add the SSH certificates as resource
Note
The certificate must be generated in PEM format. The OPENSSH format is not supported by the lib used to establish the SSH connection. You can for example use ssh-keygen -t rsa -m PEM
modules/script/scripts-1/module.resources
{
    "resources": [
        {
            "source": "root/ssh/",
            "destination": "certs"
        }
    ]
}
root/ssh/test
-----BEGIN RSA PRIVATE KEY-----
MIIG5AIBAAKCAYEAty6s/gRHdVxAky00IIxL8rIXNZYlhx9hhS7ptvIMd4vNSS0u
fBEaTDvI97xuz8B2QdrTKqR2JUWfI6VlSYD3Kc7ZZC61wQmLa2yqbKa6/b3AQ2pC
Wm5mmfw1aYvNrNuVgMwrLkXD2Bv4+qx8qVS8+oDBe8xd2YwmZXjJCMjHw/RpDhtl
r3Vj8+PbO2+vKojgd0XRoyRJUR6Kp0mUBTlhJQ+Vcq2/HUbVnxiS/AwHx0iqKsEB
d02kSFkWOJsVN2G4bsV0YFOoEDAkx54RexRvP/GoADt+4yneet2aj3/L5tsCAH3c
05lCxKFa3aW8Qn5m8DlrmJDNBWUg9beZFpjkFWlSrcOxWxuZaCk8L0DBKEcIWvDd
bFY6di+kTPPkWv069HvfKHk7DvHQekOlNIItDb66fM9cJ+K7unkYDLmB9KJYM21n
dKJW7NL0VzFGmRfLgSkZyMfl+SMsjy2R33CM41jz7BgVnelqiATBW6kpWZKGyccb
I632wGrIPO6oBYd3AgMBAAECggGAf2uNU+iAGGfCV14DO3y7u6cbs9+sXRB8Eltu
oR4/g8yQUI2IHy76XvrbMVA2uHaFDAv+BVR/BjAmoXIEQZve0Ysb9q7zKMLN4zyk
U42q1qPuIDbCzwqqfgRM1w0zVUEs/nmGs9o9f479osjmshbKmWmErOucgJ4Xe1AI
bv7SzkCt7u0pz2HV1Cm0LuTiMLEjinPbfiLYiP+4rOLmfrfKFjB/4VRwcxn5sIA0
hfSMWJf4HmNA9M7iLp0hcuCVYn+q0DhyRdRCcyA6wss4tiUtZBH1if9y8R0UFI16
i7PtgT5RzrB75Qttl17kV61CYp3tYP8S3+dHxu8X8G+LSLTn3tRHdJvtgNy9n8FE
76pK+wkR6EFGyDVMG3oPyQ4r7QEr+AWIMQmJCLkQsXTZ8q04WG88izii4+utFATn
rQ3rLymE73g7LaCHJZyUc66GmxzfOywLKkkCHmLCaK268r5TQk3wcJoUAcA3AlgV
svK1CyCQuGdXdNd24L2Ay9NmR9HJAoHBAOYU1xTWalS+3qi1h+mPszpMIcdJVR84
e8ZcNlN58rZCe1L7Fjr7H8KVZnZksWohQqLJWpzharLd6NTUGvY1LOaJ2wjXZONU
Pys8KGoPv/sVFlpgdhllFvku3Gxo7CPPgS/r4nqDyEUKvY1obX3vKsy0+Qqf4t8b
OzjLSvY5jgfHbFLP4PAuWoQNIm00xGsw1nhh4IIw0DJdqVZRZKdHtb4pKH9KVFqU
M5k2Zlq95chPWnEq3JCkKRMeg0ABVxwTbQKBwQDL0VhfZMciJ32etBcRtQ3S2edO
SRIxg9zbxb6YOpsrds88w5rhjrIfpN1Nk3UD3F0zVuAVEpBI/8sUwZNoizOTmBi9
mJMV76XG2MGHl5wgf3Pg+Z+ihrtWG7NeP8VNnj8NyZudnPqw9Rl1ed+5dEHowz1/
nIXu5drAZPlBTfG6ot2V7psiGMuAfTWeP5def0j0QGPydhuXj8LIdOsddKVXnp7i
ZdncR3JGltPsxf+lsbwW+XQbcUo5mMpuNcvmE/MCgcEAiUlMITnjjpepgl93Lq05
E4MT8LbYHN32NSEWpW6xnYFD1vrNg/oONGwzDFf+6MXZ3gppkAyNPxdcc4nwYJLQ
LOt7D+Z+Y4sEekbWEps9QZOOl/TQ40xHjf4hNmrQ5HlPq4mDxPjXSiMjgbobAzbv
geBGbcmDdP7psnTTUOJ81jVvdGZn4Mi35+1yalk/DnrArmowrV51DGiIv2Gnvozy
a/phGLsAZF/j/frQzjpbXs/Ctp4NqBzcCXV+eXWTRcRtAoHBAKC927pwGnSfPH07
fq4iYmKWI8wj6MtQOZDCJYydO99NdidwBOg6x9QZC8ewsap30rE4pMU5vL01rw4R
lJXwop6WZ3yvpeC4/b8TF54+PY2LtvIJLJLbO0ev1QhRtuN+GDBhfe8R7Mw+oPN7
SKxUOd6+i/Pml+JPOPRfLg0I0cnlxGgIpCSB9YzCMtU5RcHrFLg9SBXie+ROJso9
G2hBpFyz5o6a0PTfDAsLzNuBVBtzTum3lpBGCsnd7Fh66PHtbQKBwC93EEEPDFVA
JTPpe7EI/MQ6hR9hofCu4iFmz7w8QO+qJMzTeJpxpv49MjYv1Cq/X1Lqc/2VGS+d
MNAynmI92OGGl6W3SF5l1ZiMMAB/KRviZHwUCPlsiSB367vcchr3FEgJrg+lvZIU
AZawnGgAXO9s44GoEwwVc/AyHYY8LgeyxOKg/wFbsiL0Tl7HINbbUCvHnJstoRg5
DALrPLW3akHN8zpxaPz8vdhAs+2KOx8eJVF79W0ga2GJxfnyvlTKsw==
-----END RSA PRIVATE KEY-----
root/ssh/test.pub
ssh-rsa AAAAB3NzaC1yc2EAAAADAQABAAABgQC3Lqz+BEd1XECTLTQgjEvyshc1liWHH2GFLum28gx3i81JLS58ERpMO8j3vG7PwHZB2tMqpHYlRZ8jpWVJgPcpztlkLrXBCYtrbKpsprr9vcBDakJabmaZ/DVpi82s25WAzCsuRcPYG/j6rHypVLz6gMF7zF3ZjCZleMkIyMfD9GkOG2WvdWPz49s7b68qiOB3RdGjJElRHoqnSZQFOWElD5Vyrb8dRtWfGJL8DAfHSKoqwQF3TaRIWRY4mxU3YbhuxXRgU6gQMCTHnhF7FG8/8agAO37jKd563ZqPf8vm2wIAfdzTmULEoVrdpbxCfmbwOWuYkM0FZSD1t5kWmOQVaVKtw7FbG5loKTwvQMEoRwha8N1sVjp2L6RM8+Ra/Tr0e98oeTsO8dB6Q6U0gi0Nvrp8z1wn4ru6eRgMuYH0olgzbWd0olbs0vRXMUaZF8uBKRnIx+X5IyyPLZHfcIzjWPPsGBWd6WqIBMFbqSlZkobJxxsjrfbAasg87qgFh3c= manticore@manticore
1. Deploy the SSH key on host
To authenticate with SSH key the host must have the public key listed inside its ~/.ssh/authorized_keys file. Use one of the following method :
use ssh-copy-id from a linux host
ssh-copy-id -i [] user@host
write the public key inside the file
cat [pubkey.pem] >> ~/.ssh/authorized_keys